In healthcare, you work with the most sensitive data there is. That is why security at Wellcom is not an afterthought but the foundation: demonstrably certified, GDPR-compliant and transparent about how we work.
ISO 27001:2022
NEN 7510:2024
GDPR
EU AI Act
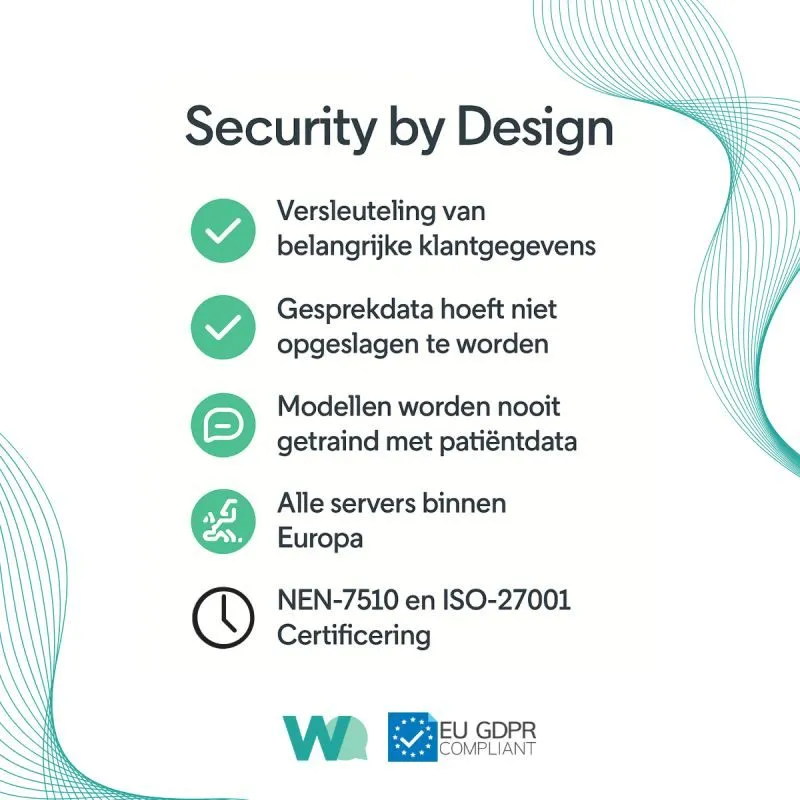
Audio not stored
No training on your data
Certified and independently assessed
Your audio is not stored.
Wellcom works alongside you in the background during the conversation and turns it straight into a report. We do not keep the recording itself; your audio is not stored. That way, the most sensitive input, the voice of the person in your care, does not stay on a server somewhere. And just as important: your conversations, reports and data are not used to train AI models.
Demonstrably secure, not just promised.
Fine words about security are quickly written. That is why we are independently assessed against the two standards that matter in Dutch healthcare.
ISO 27001:2022
International standard for information security
ISO 27001 is the global standard for information security. The certification means that Wellcom systematically identifies and manages data-related risks, from access control to incident handling, and that an independent auditor has verified this.
NEN 7510:2024
Dutch standard for information security in healthcare
NEN 7510 applies information security to Dutch healthcare practice, with specific requirements for handling medical data. For healthcare organisations in the Netherlands, it is often a firm requirement when choosing a supplier, and at Wellcom it is demonstrably in place.
Both certifications are RvA-accredited: issued by an independent body accredited by the Raad voor Accreditatie, the Dutch Accreditation Council.
We also actively put our security to the test. The cybersecurity company SecDesk examined our application in an independent penetration test, rated using CVSS v3.1: a low overall risk rating, with no vulnerabilities rated medium, high or critical. Read more (in Dutch)
Clear about data, in writing too.
Processing in line with the GDPR
We process personal data, including special categories of personal data such as medical data, in accordance with the GDPR. Our privacy statement sets out exactly which data we process, for what purpose and what rights you have.
Security is never finished. Have you found a vulnerability in our systems? You can report it safely and responsibly through our Coordinated Vulnerability Disclosure programme. We take every report seriously.
Wellcom is certified for ISO 27001:2022 and NEN 7510:2024, the Dutch standard for information security in healthcare. Both certifications are RvA-accredited: they have been assessed by an independent body accredited by the Raad voor Accreditatie, the Dutch Accreditation Council.
Is Wellcom’s security independently tested?
Yes. In addition to the certifications, we have our application independently tested by SecDesk, a specialist cybersecurity company. In a penetration test, SecDesk examined the application for possible vulnerabilities and for its resilience against cyberattacks. Severity was rated using CVSS v3.1, an internationally recognised method. The outcome: a low overall risk rating, with no vulnerabilities rated medium, high or critical.
Does Wellcom process personal data in accordance with the GDPR?
Yes. All processing of personal data takes place in accordance with the GDPR. Our privacy statement explains which data we process, for what purpose and what rights you have.
Where can I find the full security policy and the data processing agreement?
Contact us at support@wellcom-health.nl . We will gladly send you the full security policy and the data processing agreement, and answer questions from your data protection officer or information security officer.
Do you use our data to train AI models?
No. We do not use conversations, reports or other data processed through Wellcom to train AI models. They are used solely to create your report and are not shared with third parties for training purposes.
Do I need to tell my patient or client that I use Wellcom?
In the Netherlands, you do not have to. Voice-driven documentation falls within the treatment agreement between the healthcare professional and the patient or client, and therefore has a legal basis under the WGBO (the Dutch Medical Treatment Contracts Act). Explicit consent is therefore not required. The starting point is that we, as processor, do not keep any audio, transcript or summary: the report is stored only in the record, by your organisation as controller. Many healthcare professionals simply mention it anyway, as it builds trust.
Does Wellcom fall under the MDR?
No. Our applications serve a purely administrative and supporting purpose: we do not analyse or diagnose, and we do not perform any medical acts that are classed as a medical device. As a result, they fall outside the scope of the Medical Device Regulation.
How does Wellcom relate to the EU AI Act?
Our solutions are designed around the AI Act’s requirements for transparency, risk management and reliability. For example, you see the text appear in real time as you speak, and you always review the report yourself before it goes into the record.
Can colleagues see each other’s conversations and reports?
No. By default, conversations and reports are only accessible to the person who created them. With user groups and access rights, your organisation decides who can see what, and at organisation level you set those rights per user or per location.
Are my audio recordings stored?
No. Your audio is not stored: Wellcom turns the conversation into a report and does not keep the audio recording itself. Want to know more about how reports are stored, access and retention periods? Contact us at support@wellcom-health.nl for the full security policy and the data processing agreement.
Wellcom had its application independently tested by SecDesk. The penetration test resulted in a low overall risk rating, with no vulnerabilities of medium, high or critical risk.
Read more
→
Questions about security?
Would you like to see the security policy, request a data processing agreement or check our certificates? Email us and we will gladly help your information security officer or data protection officer.